Sign in. It’s quick, free and it’s up to you.
An account is an optional way to support the work we do. Find out more.
Sign in. It’s quick, free and it’s up to you.
An account is an optional way to support the work we do. Find out more.
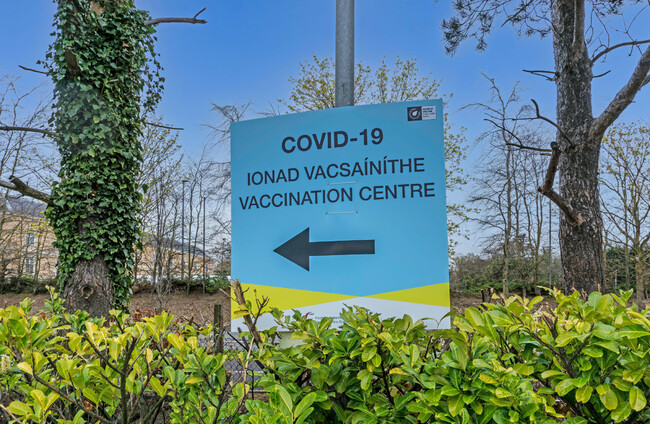
THE HSE HAS said a “misconfiguration” of its electronic dataset related to the roll-out of the Covid vaccine did not result in the “unauthorised accessing or viewing” of personal data.
The Covax system is an electronic dataset which records all Covid-19 vaccinations in Ireland and was used “for statistical and activity analysis”.
The data collection start date was 27 December 2020 and the HIQA website states that it “continues to this day”.
The data includes “person-identifying information” of individuals, as well as data on citizens who were not vaccinated by virtue of non-attendance.
HIQA adds that the data in Covax is accessed by staff in the National Immunisation Office for “the purpose of data curation and vaccination programme management”.
The “misconfiguration” is said to have occurred in December, 2021.
In a statement to The Journal, the HSE said “security considerations were at the forefront of the Covax deployment”.
However, the statement added that “when a system of this nature is put together under time pressure (as was the case as we established the Covid-19 vaccination campaign), misconfigurations can occur”.
“In this case an external source pointed out one misconfiguration which would have required deep technical expertise to exploit,” said the HSE spokesperson.
They added that the misconfiguration was “remedied” on the day the HSE were alerted to it.
“If someone accessed data, we would be able to see this in the detailed logs which we analysed,” said the HSE.
“Apart from the source who informed us of this issue, there was no unauthorised accessing or viewing of this data.”
The HSE said the data accessed was “insufficient to identify any person without additional data fields being exposed”.
As a result, the HSE said a Personal Data Breach report to the Data Protection Commission was not required.
In a statement to The Journal, a spokesperson for the Data Protection Commission said the “DPC has only become aware of this issue within the last 24 hours, and we will be engaging with the HSE on it”.

To embed this post, copy the code below on your site


have your say