Sign in. It’s quick, free and it’s up to you.
An account is an optional way to support the work we do. Find out more.
Sign in. It’s quick, free and it’s up to you.
An account is an optional way to support the work we do. Find out more.
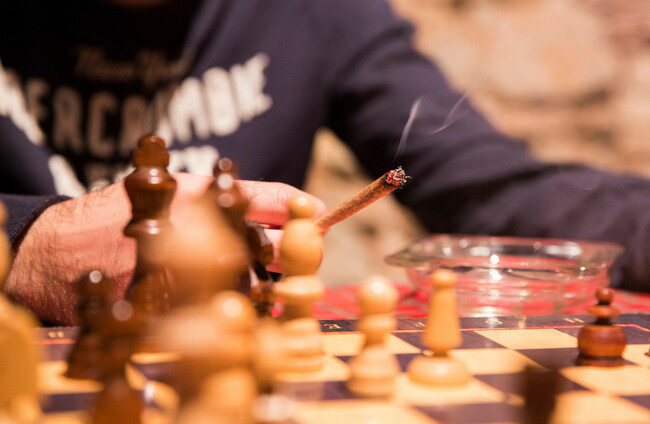
VULNERABILITIES FOUND IN an online database may have seen as many as 12,000 Irish passports sitting in the open and at risk of being picked up by hackers.
The passports are believed to have belonged to users of so-called ‘cannabis members-only clubs’ in Spain. They are understood to be among almost one million passports and photo IDs that could be publicly accessed for a period in May and June, and potentially longer.
An Irish-registered software company called Cannabis Club Systems (CCS), also known as Nefos Solutions, was in charge of the data.
The Data Protection Commisisoner’s office told The Journal that it has been engaging with the company after the concerns came to light.
The company has said there was no evidence that any outsider accessed the data after the initial vulnerability was reported.
CCS develops and provides the software that Spanish cannabis clubs use for everything from sales to membership admissions. This includes a system where receptionists upload IDs to a cloud system for additional verification.
Cannabis clubs are somewhat common in cities across Spain, with some estimates putting the number at between 1,000 and 2,000.
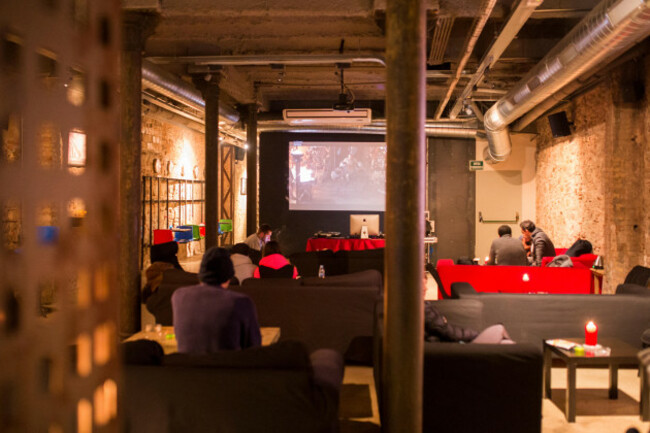
Unlike commercial dispensaries or the open coffee shops found in Amsterdam, these clubs operate on a membership-only model. You need to register with the club and show proof of age before you can consume cannabis on the premises.
However, this has meant that the details of some 985,000 club members may have been jeopardised by the recent leak.
A listing compiled by a security researcher testing the database’s security collected the number of nationalities involved – it included 12,000 Irish passports, along with 30,000 from the US.
CCS has been contacted on a number of occasions by The Journal in recent weeks, but has not responded in time for publication.
The company, which was incorporated in Ireland ten years ago, has an address listed at an office at Harcourt Street in Dublin 2.
In a statement on its website in June, its chief technology officer Andreas Nilsen said that it had “temporarily suspended” backend services for its platform while it reviewed its security.
Nilsen said that “vulnerabilities were identified and remediated”, but that CCS had not found any evidence that personal information was publicly leaked, published, or distributed.
“Investigations into the historical extent of any unauthorised access remain ongoing,” he said at the time. The company has not issued a public update since, including when contacted by The Journal.
He stressed that “reported vulnerabilities have been remediated and the previously identified endpoints are no longer accessible” by members of the public.
CCS “takes the privacy and security of personal information extremely seriously”, Nilsen continued.
The senior executive said that CCS has worked with regulated cannabis organisations across multiple jurisdictions for over 12 years, and understands that it operates within a “highly sensitive compliance environment”.
“Protecting confidential information remains one of our highest priorities, and we continue to invest in strengthening our security infrastructure and governance processes,” Nilsen said.
There has been no finding of wrongdoing by the DPC in the case.
In June, US tech website The Verge reported that hundreds of thousands of passports for people who used cannabis clubs in Spain could be accessed via a ‘backdoor’ into its database.
The issue came to light after a security researcher allegedly discovered the multitude of passports and IDs sitting unprotected at public URLs, reportedly with no password access required.
This happened, according to The Verge, because a ‘secret key’ for processing payments was sitting inside an app used by the cannabis clubs.
Brian Honan, a Dublin-based security expert who works across the public and private sector, told The Journal that this can be an all too common occurrence in instances where data was inadvertantly shared.
“It’s basically like somebody has put the key under the doormat, but anybody with access to the doormat can get in. It isn’t good practice to have your key stored in the application,” Honan said, referring to the report containing the allegations.
Nilsen had said in the initial report that there was no evidence that any outsider accessed the data other than the security researcher who discovered the open database.
He added to that the company would “communicate to everyone that was potentially exposed”.
Honan, the data security analyst, warned that companies could face hefty fines if data is found unsecured, as passport leaks could place people at the mercy of scammers.
Honan noted that the use of the cannabis could be categorised as for medicinal purposes, which Spanish cannabis clubs include as part of their membership.
Under GDPR legislation, Honan said that the health data would be deemed to be particularly sensitive, especially if it was “freely available on the internet”.
“There is obviously a lot of sensitive, personal data stored in that system. People’s IDs give a lot of information and that can be of use to criminals for scams,” Honan said.
Given the Spanish system allows people to buy cannabis, their country of origin and the laws in place around drug use in those jurisdictions could also be a factor in any risk.
“The individuals themselves could be at risk, either potentially from scammers who could blackmail you because they have that information, or authorities who could come across that information,” Honan added.
The EU’s GDPR laws can carry tough punishments for health data breaches, with penalties of up to €20 million or 4% of global annual turnover a danger to a company.
When asked how common such alleged data breaches, as seen in the Spanish cannabis clubs can be, Honan said they remain an issue for many companies handling sensitive information.
“The challenge we have is that we have many developers who are very good at writing code, but writing secure code is not as widespread as it should be,” Honan said.
“The onus is not just on the company developing an application or software securely, but under GDPR the company providing the application and the company requesting the development are required to build in privacy and security by design.”

To embed this post, copy the code below on your site


have your say