Sign in. It’s quick, free and it’s up to you.
An account is an optional way to support the work we do. Find out more.
Sign in. It’s quick, free and it’s up to you.
An account is an optional way to support the work we do. Find out more.
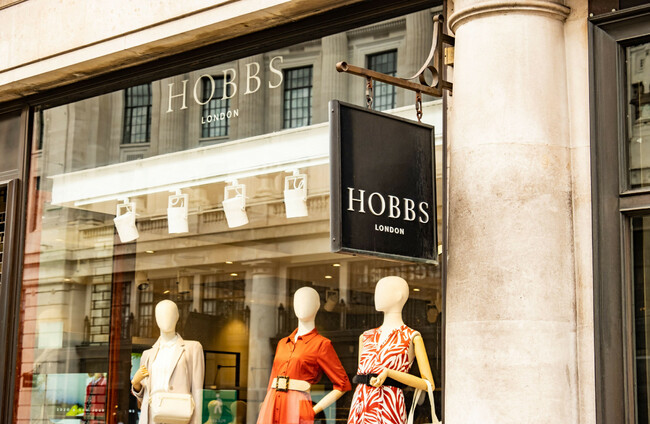
THE PARENT COMPANY of fashion brands Hobbs, Phase Eight and Whistles has apologised to customers after being hit by a cybersecurity incident.
TFG London said it had identified an incident affecting some of its IT systems on Sunday, 11 October, but added that there was currently “no reason to believe that payment information is at risk”.
The incident could affect customers in Ireland, as Hobbs has a number of stores across the country and Phase Eight clothing is sold through several retail outlets.
In an email to customers, the company said: “On Sunday 11 October, TFG London identified a cybersecurity incident affecting some of our IT systems.
“As soon as we identified the incident, we activated our business continuity plan, engaged external cybersecurity experts and informed relevant authorities.
“Our investigation is ongoing, and we are working hard to get all our systems back up and running as quickly and safely as we can.
“All our stores are open as normal, and our teams will be happy to welcome you.”
The company warned that orders placed on or after Sunday may be delayed, but urged customers not to place their orders again.
TFG London said payment processing was carried out by a third-party provider and that, based on its investigation so far, it had no reason to believe payment information was at risk.
However, it said it was still working to establish whether any sensitive customer information had been affected.
“If we determine that your personal information was affected, you will be directly informed. We do not believe it is necessary to change your account login information at this time,” the company said.
“We know this news may be unsettling, and we’re committed to keeping you updated as we have more information to share.
“We are very sorry for any inconvenience this incident has caused.”
The incident comes just a week after online fashion retailer ASOS confirmed that some customers’ personal information had been accessed in a separate cyberattack.
ASOS said an unauthorised party had gained access to an employee’s account and used it to access information held on third-party platforms. The retailer confirmed that names and contact details had been accessed, but said payment card information and account passwords were not affected.
Additional reporting from Andrew Walsh

To embed this post, copy the code below on your site


have your say